
Learning bite
VMs and containers
Choose an environment according to the operating-system behavior you need to study.
 Linux
Predict before you try
Does installing a kernel package in an ordinary application container replace its running kernel?
Try it: Try three placement decisions →On this page
The kernel boundary changes the exercise
A conventional VM boots its own guest kernel. A Linux container isolates processes using facilities such as namespaces and resource controls while sharing its host Linux kernel. An image can contain a distribution's userspace without containing a separately booted kernel.
| Question | Full VM | Typical application container |
|---|---|---|
| Who supplies the running kernel? | Guest installation | Container host |
| What normally starts? | Guest init and services | Selected application process |
| Where is persistent data? | Guest disks and external storage | Explicit mounts/volumes or external services |
| How is an update delivered? | Guest maintenance or image replacement | Usually a rebuilt image and replacement container |
These are practical defaults, not claims that every VM or container is configured identically.
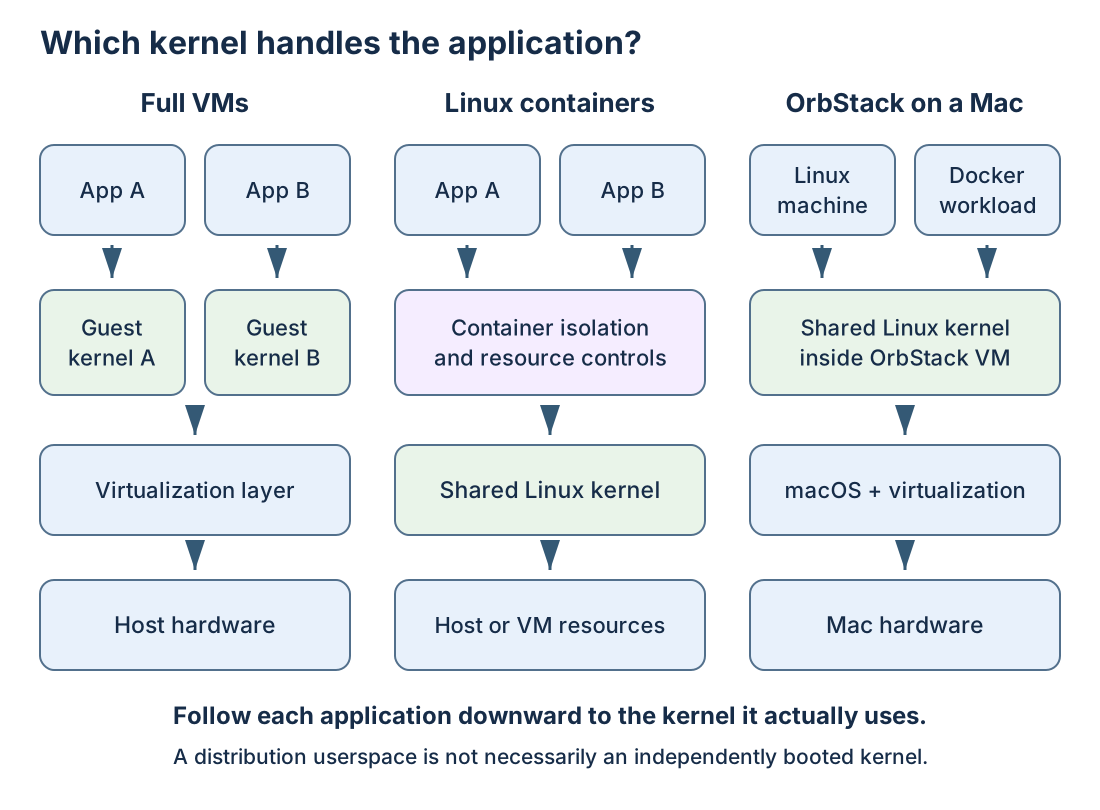
Read downward from each application to the kernel handling its system calls. In the VM example those paths reach separate guest kernels. In the container example they converge on one Linux kernel. The Mac example adds a Linux VM because macOS itself does not supply Linux system calls.
An image is packaged filesystem content and metadata used to create an environment. A container is a running or stopped instance created from an image. Linux namespaces give processes different views of resources such as process IDs and networking. Resource controls, commonly cgroups, account for and limit their use. Those controls do not mean each container has a separately booted kernel.
For example, a container can report Ubuntu in /etc/os-release while uname -r reports its host's Linux kernel. The files describing userspace and the running kernel answer different questions. A writable container layer is also not automatically a durable backup; persistent data needs a deliberately retained volume, mount, or external store.
Linux containers on a Mac
macOS does not provide a Linux kernel directly to Linux containers. OrbStack supplies a Linux VM and Docker integration. Its lightweight Linux machines also share that Linux kernel. They are useful for many distribution and service exercises, but they are not independent full VMs with separate boot chains.
Keep that distinction in your notes when comparing uname -r with /etc/os-release: the first describes the running kernel, the second describes the installed userspace distribution. Different distributions can report the same shared kernel.
Match the lab to the boundary
Use OrbStack for file permissions, processes, systemd services on Ubuntu, package management, and Ansible practice. Use a full VM with its own bootable guest kernel for bootloader repair, independent kernel replacement, or a realistic disk-layout/LVM experiment. A Docker application container is useful for packaging and runtime lifecycle work later in DevOps foundations.
Try three placement decisions
For each task, pick an environment and explain the kernel/lifecycle reason:
- Change a configuration file and inspect a systemd service: the Ubuntu OrbStack machine is suitable because it supplies the distribution userspace and service manager needed here.
- Repair a guest bootloader after a failed kernel boot: use a full independently bootable VM with console recovery; neither an ordinary application container nor an OrbStack shared-kernel machine demonstrates this.
- Package one web process reproducibly: an application container is a useful later DevOps exercise, with persistence and networking made explicit.
The answers depend on what must be observed, not on the presence of a shell prompt. Do not launch three environments to complete the exercise; draw them and justify the choice. Next, create only the single Linux learning machine.
Check and revise
Does installing a kernel package in an ordinary application container replace its running kernel? No. Does having a shell inside a container make it equivalent to a VM? No: inspect isolation and lifecycle boundaries.
Revision: choose by the behavior under test, not by whichever environment starts fastest. This comparison creates no resources and makes no claim that the later kubeadm topology has already been validated on OrbStack.
Apply this to MicroBank
For MicroBank, distinguish application containers from the Linux environment that supplies their kernel. A container image describes packaged files and runtime settings; it is not an independently booted VM. Sketch Accounts and Ledger beside their database dependencies. Keep the sketch labelled as a future deployment until the DevOps implementation lab creates and checks those processes.
Keep this observation in the MicroBank readiness project.
Sources
Primary references: Container fundamentals↗; OrbStack architecture↗.
Prove what you learned
Inspect the result
Compare machine identity, package state and an operation before and after the exercise.
Explain it in your own words
Explain why your observation supports the stated outcome, and name one thing it does not prove.
Try a small variation
Explain how the same observation would differ on a full VM and an OrbStack Linux machine.
Your evidence should show
- Record the context/revision or label the work as a paper or prepared fixture.
- Compare the prediction with the actual result from “Try three placement decisions”.
- Compare machine identity, package state and an operation before and after the exercise.
- Explain the transfer challenge and retain the same verification question.
Hint
Separate host, virtualization boundary, guest userspace and running kernel.
Answer guide: compare after predicting
No. Does having a shell inside a container make it equivalent to a VM
Compare this with your actual observation. A paper answer is useful reasoning practice; record execution separately.
Recall process and request boundaries from the opening module. Revisit the previous lesson.
Save the prediction, result and explanation ↓Your notes and evidence
Record observations, questions, or links to your work. Keep credentials out of your notes.
Back up or restore this path
Progress and notes stay in this browser. A backup contains only this learning path.